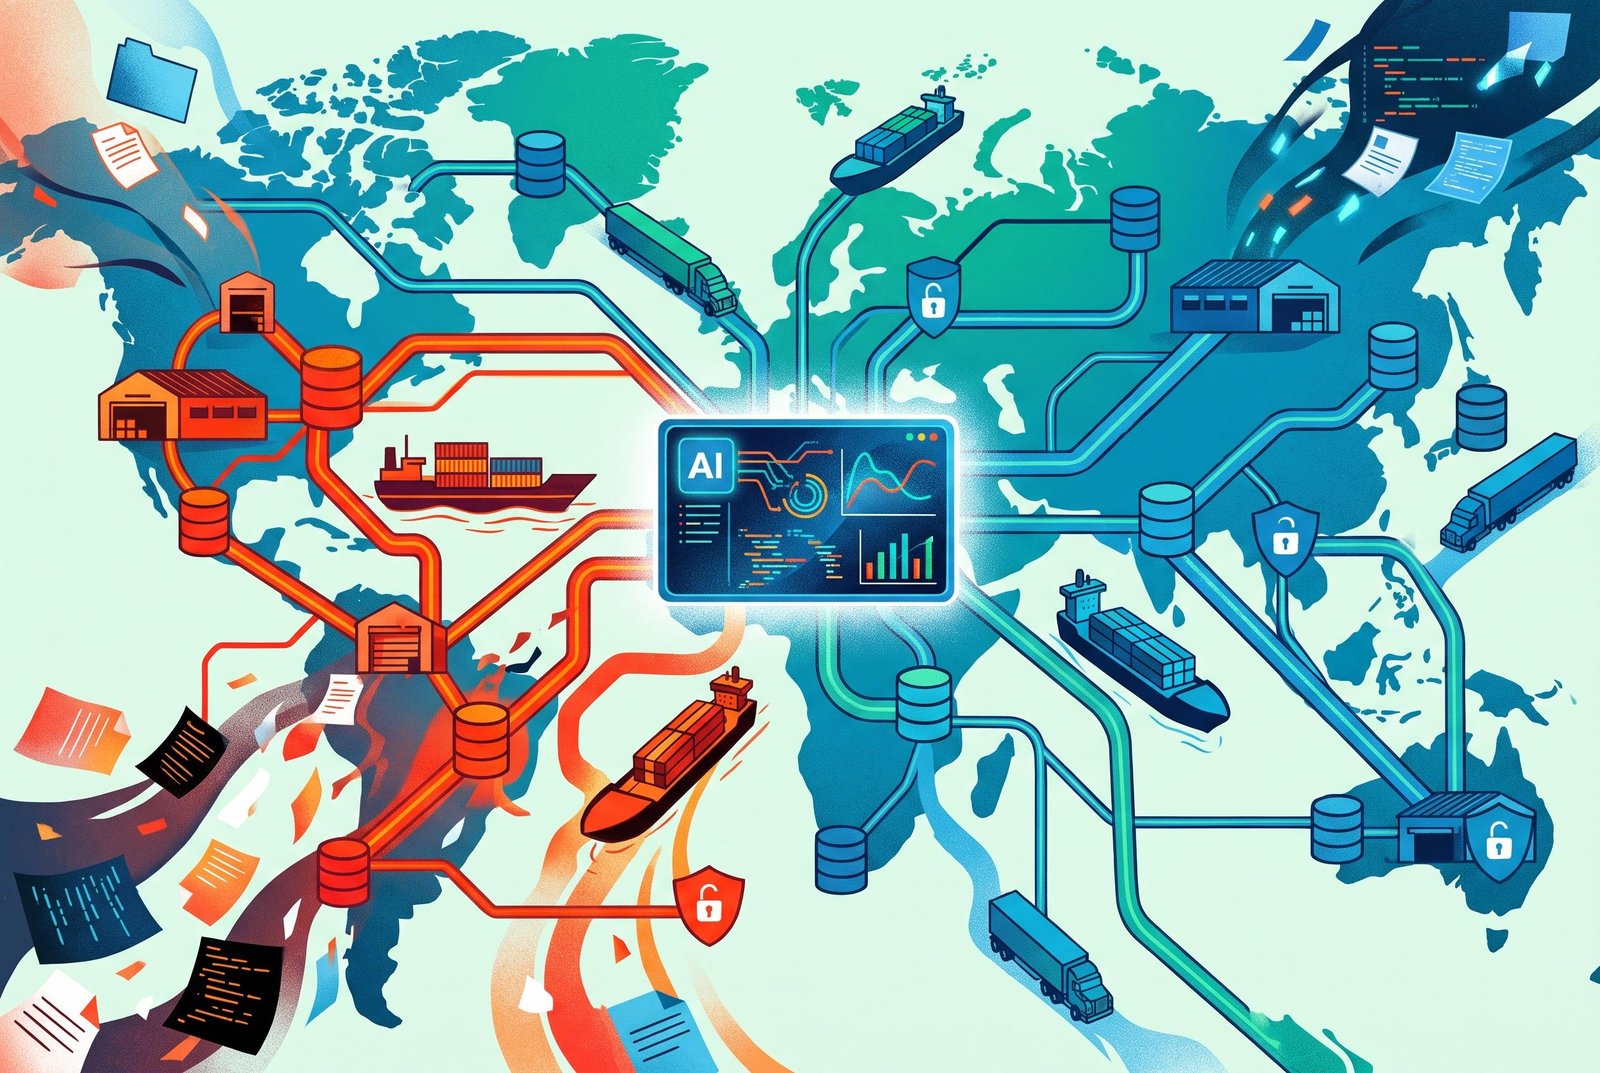
A survey of 250 managers and senior professionals at organisations using AI in supply chain, logistics, distribution and wholesale found that roughly one in six said their company had experienced an incident in the previous year in which an AI tool exposed supplier or customer data, shared it, or allowed access by someone who should not have had it.
The figures come from Instalily, a provider of business AI agents, whose report, “Shared Risk: Why Supply Chain’s Most Sensiti...
Continue Reading This Article
Enjoy this article as well as all of our content, including reports, news, tips and more.
By registering or signing into your SRM Today account, you agree to SRM Today's Terms of Use and consent to the processing of your personal information as described in our Privacy Policy.
ve Data Needs AI Built for the Industry”, draws on responses collected on 9 October. The results point to a particular challenge for businesses that handle confidential information on both sides of a transaction: AI systems may be able to reach records that reveal the commercial terms between customers, suppliers, carriers and intermediaries.
According to the survey, 78% of respondents said their AI tools could access customer prices and margins, while 67% said the tools could reach supplier prices and rebate information. Some 63% reported at least some overlap between supplier and customer data across company platforms, including AI tools. Despite this, 87% said they were very or somewhat confident that their systems kept the information properly separated.
Instalily said incidents had been reported across every industry segment included in the survey. Potential consequences range from one customer seeing another’s negotiated price to a competitor obtaining a supplier’s bid, or a shipper discovering the underlying carrier rate behind a broker’s margin.
The risks are not confined to supply chains. OWASP, the Open Worldwide Application Security Project, warns that large language model applications can reveal sensitive information through generated responses. It identifies financial and confidential business records among the information at risk, and cautions that prompt instructions alone are not a complete defence: they can fail or be bypassed, including through prompt injection. Its guidance points to the need to limit sensitive data in inputs and outputs, handle information carefully and give users clear direction on secure use.
The National Institute of Standards and Technology likewise treats AI risk management as an ongoing process, to be considered across design, deployment, use and evaluation. Its voluntary framework offers organisations a structure for assessing issues including security, privacy, reliability and accountability, rather than a certification of any particular product.
Instalily recommends testing safeguards through ordinary business tasks, such as producing a customer quote without disclosing confidential supplier terms, and defining which actions should require human approval. The company says its Lily platform works within existing business systems and uses access permissions and audit records to support oversight.
The vendor also describes options including deployment in a customer’s cloud environment or a dedicated instance, approval workflows for specified high-risk actions, and logging of agent activity. Its security page says each customer is assigned a separate Google Cloud project and that data is not used to train models across customers. These are Instalily’s own descriptions of its safeguards, not independent evidence of their effectiveness; the company notes that some controls depend on customer configuration and implementation.
For businesses evaluating AI tools, the broader lesson is that permissions alone may not settle whether information stays appropriately contained. Controls need to be examined throughout a task, from the records an agent can retrieve to the response it produces and any action it takes.
Source: Noah Wire Services